Many Indian IT and SaaS companies lose deals without knowing the real reason. Clients often ask about data security before signing any contract. SOC 2 compliance answers that question with proof, not promises. Companies without this certification often get quietly dropped from vendor shortlists. Global clients expect it as a baseline, not a bonus. This blog explains why SOC 2 compliance matters and how it protects business growth.
What Is SOC 2 Compliance?
SOC 2 is a security framework created by the AICPA. It checks how a company handles customer data. The framework looks at security, availability, and confidentiality. An independent auditor reviews the company’s systems and processes. If everything meets the standard, the company receives a SOC 2 report. This SOC 2 certification report becomes proof of trust for clients and partners.
Why Clients Are Asking for It Now
Client expectations have changed over the past few years. Data breaches and leaks have made buyers more careful. Companies now ask vendors to prove their security practices upfront. This is common for clients based in the US, UK, and Europe. Indian firms working with global clients feel this pressure directly. Even domestic clients in cities like Bengaluru, Pune, and Hyderabad are starting to ask for it. Without SOC 2, many vendors get removed early in the selection process.
How SOC 2 Certification Impacts Deal Closures
Sales teams often see deals stall at the final stage. Legal and security teams on the client side step in and ask for compliance proof. If a company cannot show SOC 2 certification, the deal slows down or stops. This delay can cost months of sales effort. Some companies lose the deal entirely to a certified competitor. SOC 2 removes this risk by answering security questions before they are even asked.
Key Benefits for IT and SaaS Companies
Beyond winning deals, SOC 2 compliance brings real operational value. Companies that go through the process build stronger internal systems.
- Builds trust with enterprise and global clients
- Reduces time spent on security questionnaires
- Strengthens internal data handling practices
- Improves employee awareness around security
- Creates a clear audit trail for future certifications
- Gives sales teams a strong point during negotiations
These benefits add up over time, not just during one deal cycle.
“ISIT Consultants helps IT and SaaS companies turn SOC 2 compliance from a stressful checkbox into a powerful trust signal that opens doors to bigger clients and long-term global partnerships.”
SOC 2 Type I vs. Type II: Understanding the Difference
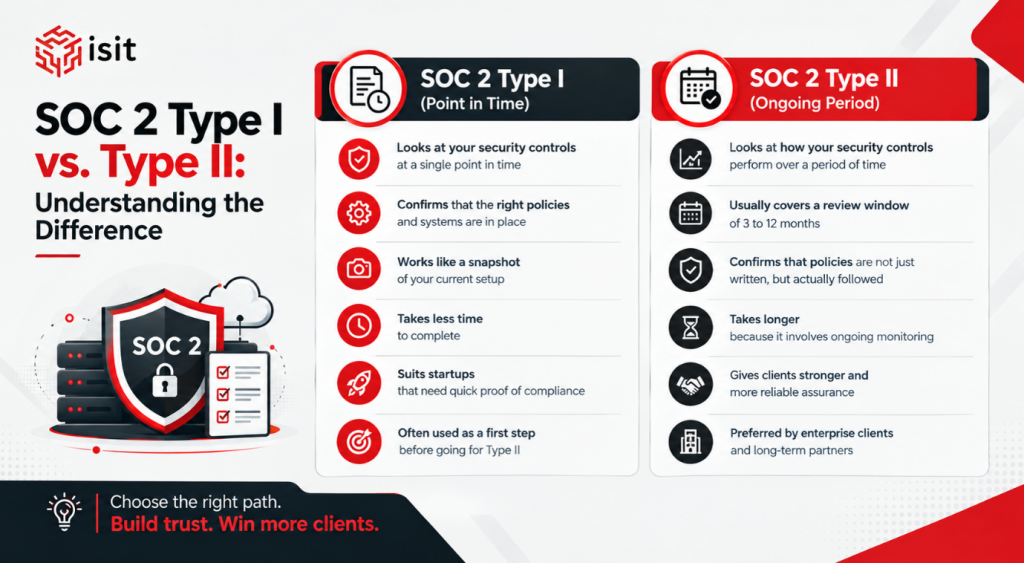
Many business owners hear about SOC 2 and assume it is just one certification. In reality, there are two types, and the difference matters a lot. Choosing the right one depends on your business stage and client expectations. Here is a simple breakdown to help you understand both.
SOC 2 Type I
- Looks at your security controls at a single point in time
- Confirms that the right policies and systems are in place
- Works like a snapshot of your current setup
- Takes less time to complete
- Suits startups that need quick proof of compliance
- Often used as a first step before going for Type II
SOC 2 Type II
- Looks at how your security controls perform over a period of time
- Usually covers a review window of 3 to 12 months
- Confirms that policies are not just written, but actually followed
- Takes longer because it involves ongoing monitoring
- Gives clients stronger and more reliable assurance
- Preferred by enterprise clients and long-term partners
If your company is new to compliance, Type I is a good starting point. It shows clients that you take security seriously and have proper systems ready. As your business grows and works with bigger clients, Type II becomes more important. It proves that your security practices are consistent, not just documented on paper.
Many companicredibility. This step-by-step approach also makes the certification process easier to manage, instead of trying to achieve everything at once. Understandinges follow a natural path. They start with SOC 2: Type I to build early trust. Once they are ready, they move to SOC 2: Type II for stronger, long-term this difference helps you plan your compliance journey with more clarity. It also helps you set the right expectations with clients who ask about your SOC 2 status.
Common Roadblocks During Certification
Many companies delay SOC 2 certification because the process feels complex. Teams often do not know where to start or what documents are needed. Internal policies may be missing or outdated. Employees may not follow consistent security practices across teams. Smaller companies sometimes lack a dedicated compliance person. These gaps slow down the certification timeline if not addressed early.
Steps to Get SOC 2 Compliance Ready
Getting ready for SOC 2 does not have to feel overwhelming. A clear, guided approach makes the process smoother.
- Identify the right SOC 2 report type for your business
- Review current data security policies
- Fix gaps in access control and monitoring
- Train employees on security practices
- Prepare documentation for the audit
- Work with experienced consultants to guide the process
Following these steps in order reduces delays and confusion.
Key Takeaways for IT and SaaS Founders
- SOC 2 compliance builds direct trust with global and enterprise clients
- Deals often stall or get lost without proper certification
- Cities like Bengaluru, Pune, and Hyderabad are seeing rising demand for compliance-ready vendors
- The certification process also strengthens internal security practices
- Common delays come from missing policies and unclear ownership
- A step-by-step approach makes certification manageable for any team size
Conclusion
SOC 2 compliance is no longer optional for IT and SaaS companies in India. It protects deals, builds trust, and strengthens internal systems. Companies that delay it often lose ground to competitors who are already certified. ISIT Consultants works with growing IT and SaaS firms to make this process simple and stress-free. If client trust matters to your business, now is the right time to start the SOC 2 journey.

